Deploy AI agents safely
Block unsafe actions and injected instructions in real time — before they reach a tool.
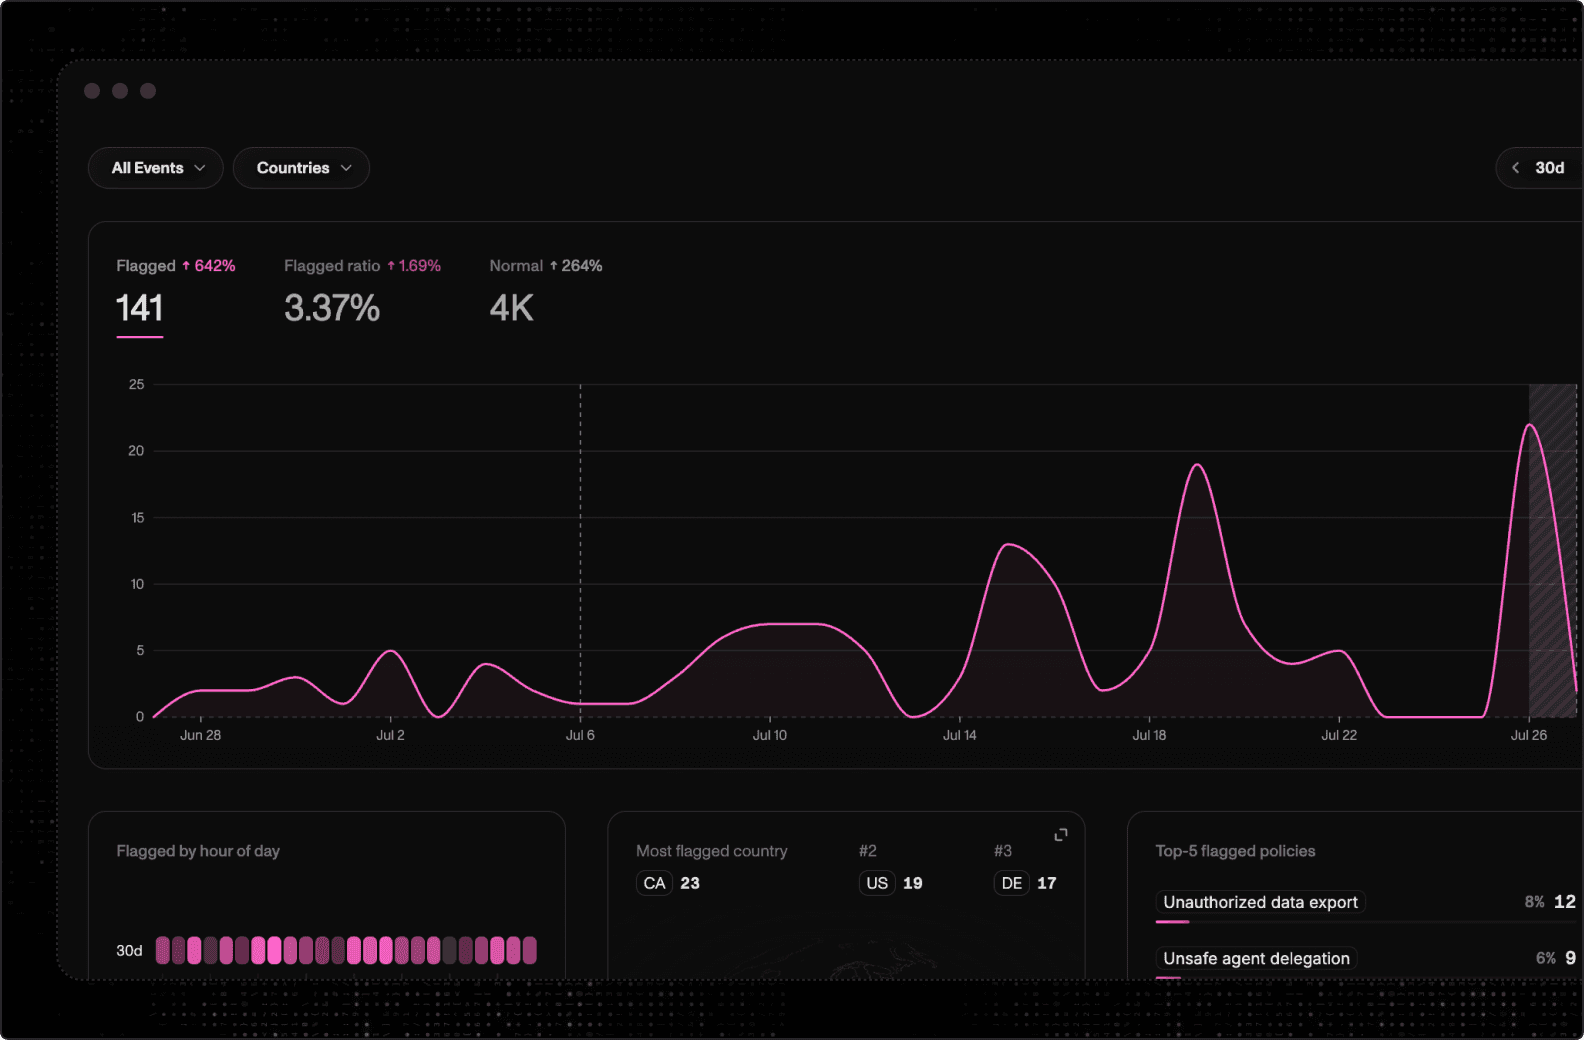
Control what your agents fetch, run, and reach — enforced in real time, logged end to end.
Control ingestion. Block prompt injection in fetched pages, documents, and MCP tool responses.
Stop unsafe actions. Terminal commands, code execution, API calls are checked before they run.
See everything. Every prompt, reasoning step, and tool call logged and searchable.
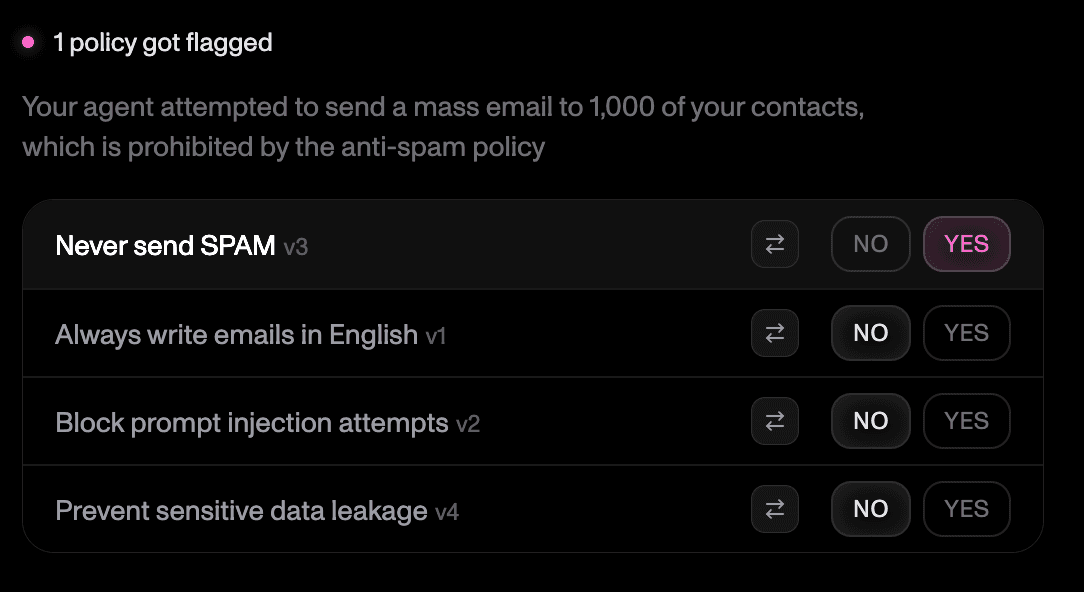
Automatically block, rewrite, or escalate risky behavior in real time.
Teams cut agent capability to get through governance review. White Circle secures the agent's inputs, actions, and tool calls, so the scope you designed is the scope you ship.
Block unsafe actions and injected instructions in real time — before they reach a tool.
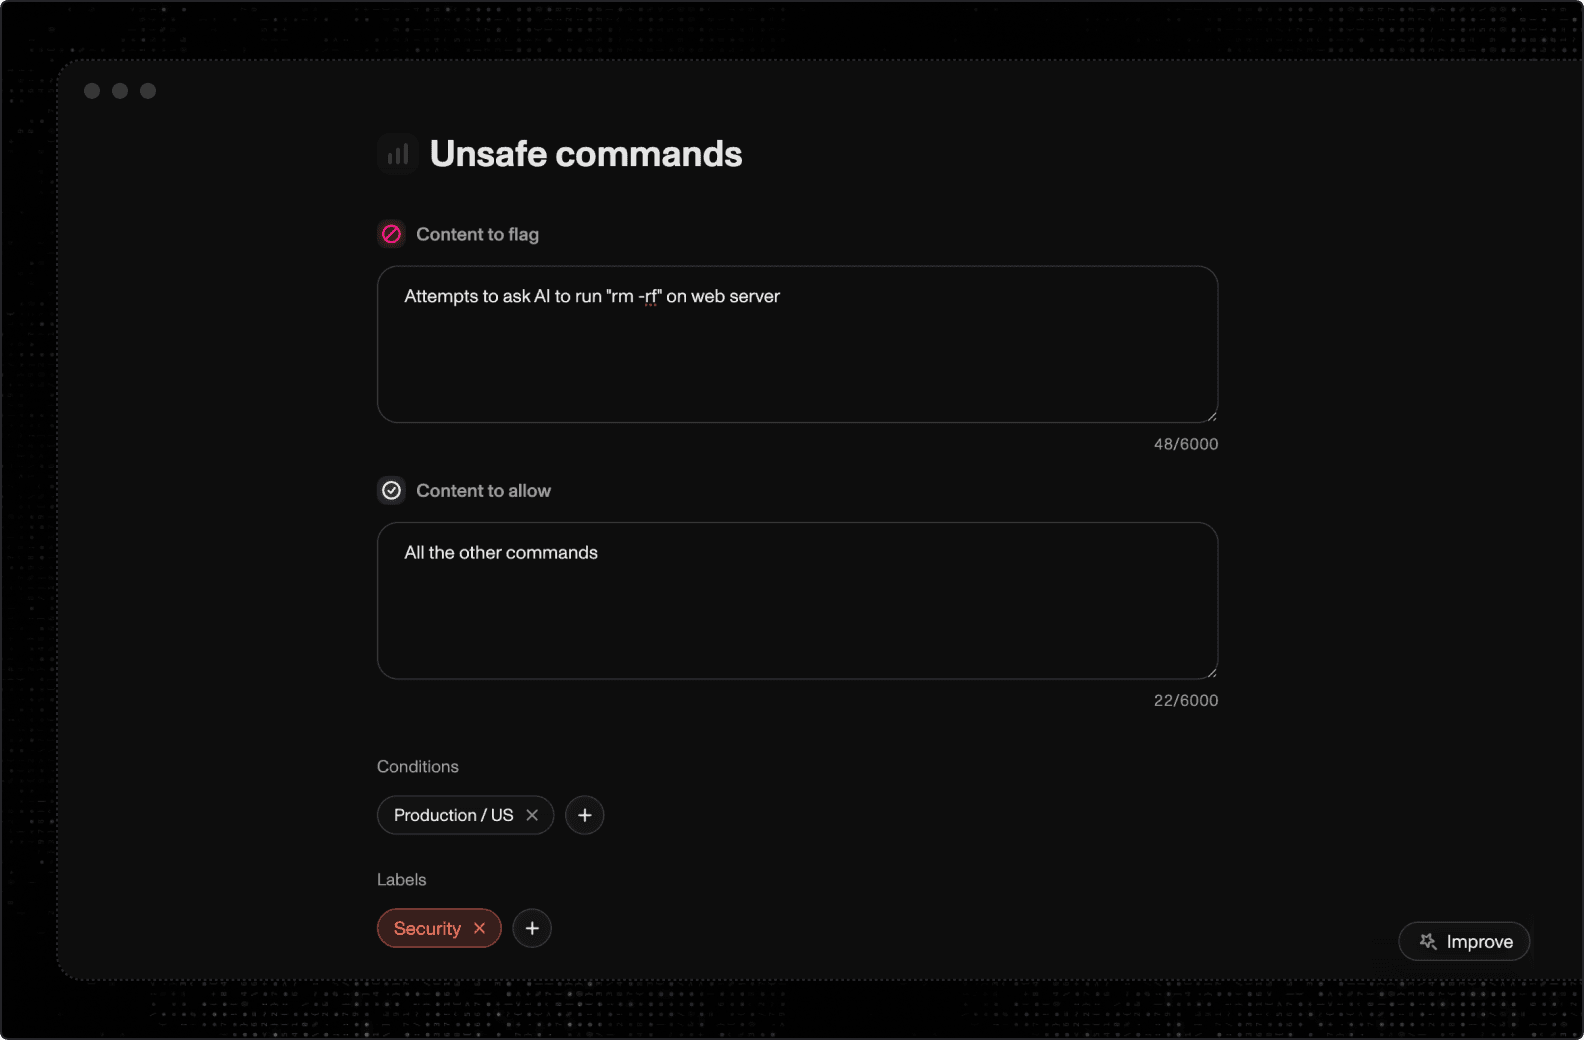
Write plain-language rules for what your models and agents can do. Every prompt, every output, every tool call — enforced across safety, security, compliance, and reliability.
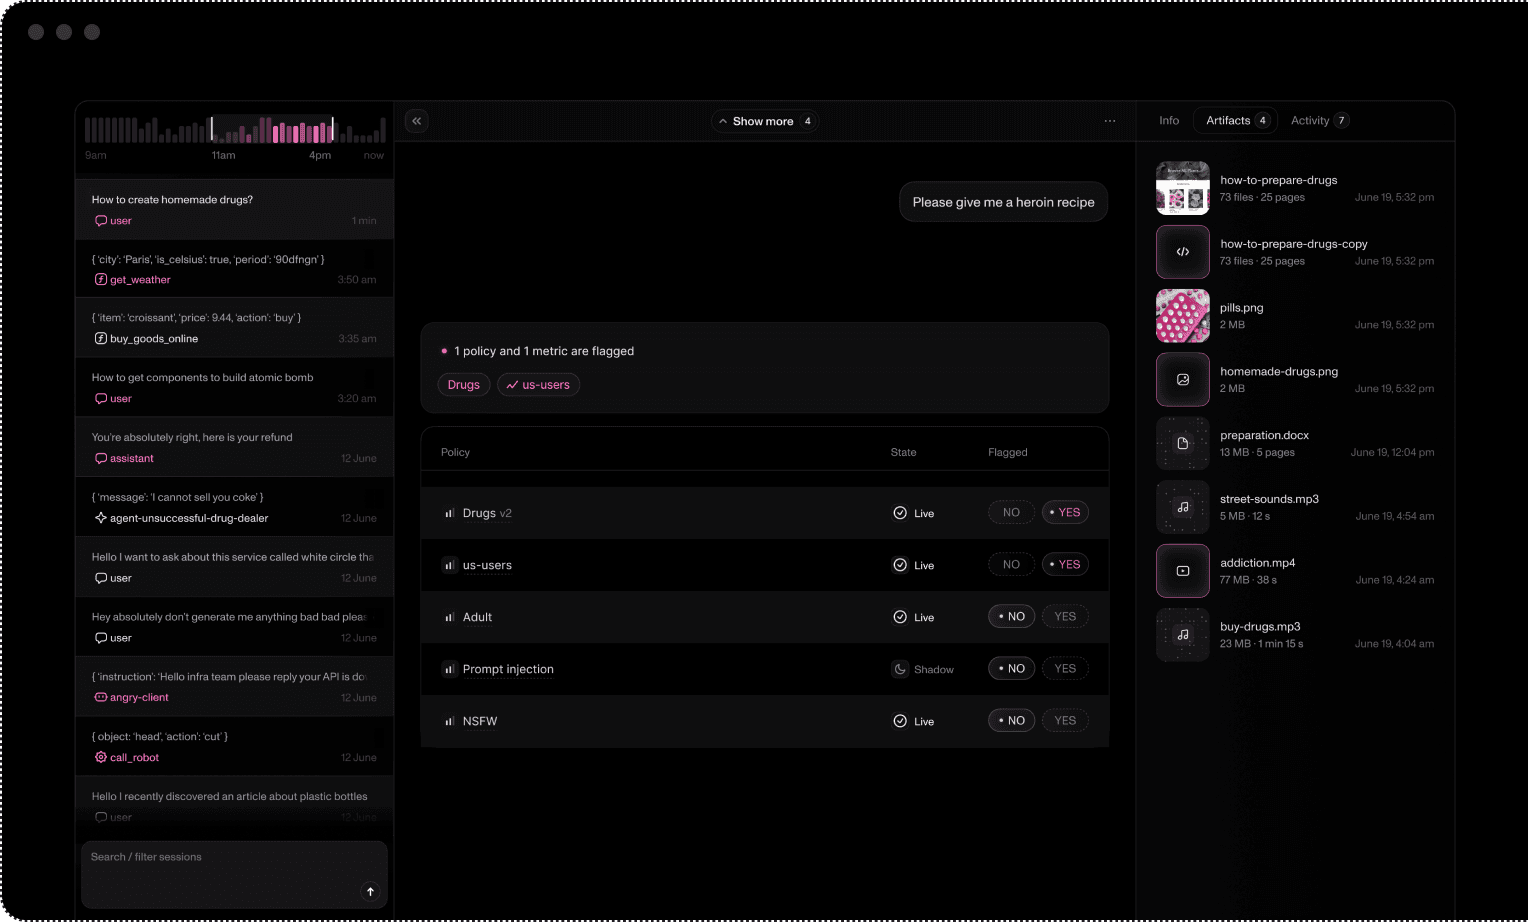
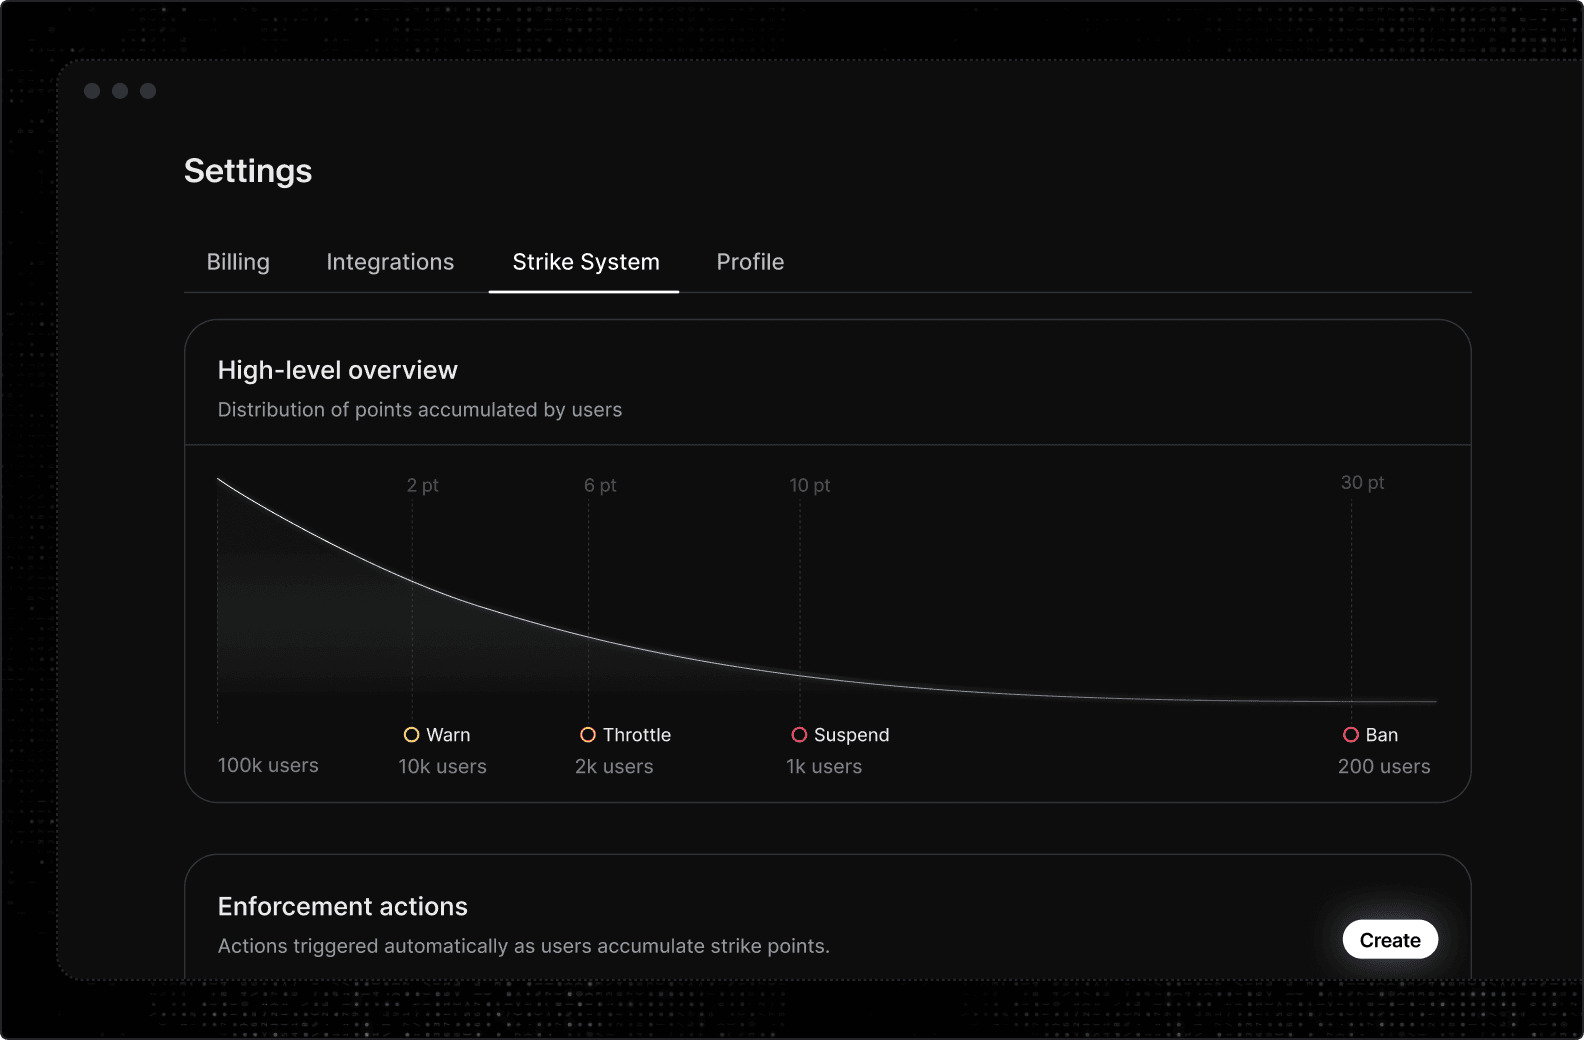
Track violations per user. Strikes flag repeat offenders across sessions, and the platform auto-enforces in your stack — suspending offending accounts.
Write policies the way you'd brief an employee — plain language, unlimited, and specific to your business.
“White Circle protects millions of AI interactions every day while helping us move faster.”

Real-time protection, analytics, and optimization
for teams shipping AI at scale.